




 South Carolina · United States
WONE Global Partner · United States
Sourced guides to doing business in each market, and the status of every service there. Partners are in place in 35 markets so far.
One WONE Global Partner for each service in each market. Start from what you need to do, or go straight to a service.
Describe what you need. WONE Global names the service and the professional before any work begins.
Bring a requirement →Licences, value chains and the questions businesses in each industry ask first, with the services that usually apply.
What one country changes for the other, worked journeys step by step, and who handles each side.
When cross-border business becomes a dispute, UNIONE™, also part of the UNBOUNDED™ Global Ecosystem, prevents it, resolves it, arbitrates it and plans enforcement. 334 Fellows in 58 countries.
41 jurisdictions, each with primary sources and the date last checked.
Named senior professionals, each admitted as the one firm for a service in their country, and the firms they lead.
One Partner per service, per jurisdiction, admitted by review against published criteria.
Every statement is labelled: source-checked, professionally reviewed or not yet checked, with its source and date where checked.
Answers cite WONE Global's sourced statements and show how each one was checked. Research, not advice.
Accomplished regional specialists and international cross-border intelligence, across 100 countries, with one contact and one published Standard.
United States × Technology, Data & Cyber
Data, cyber and technology rules for running a digital business internationally. In the United States, that means local law, local regulators and local practice, handled by a qualified professional who practises there.
On request
No WONE Global Partner holds this yet. Send us your requirement: WONE Global confirms whether a vetted Associate firm can act, tells you who it is and checks for conflicts before any work begins.
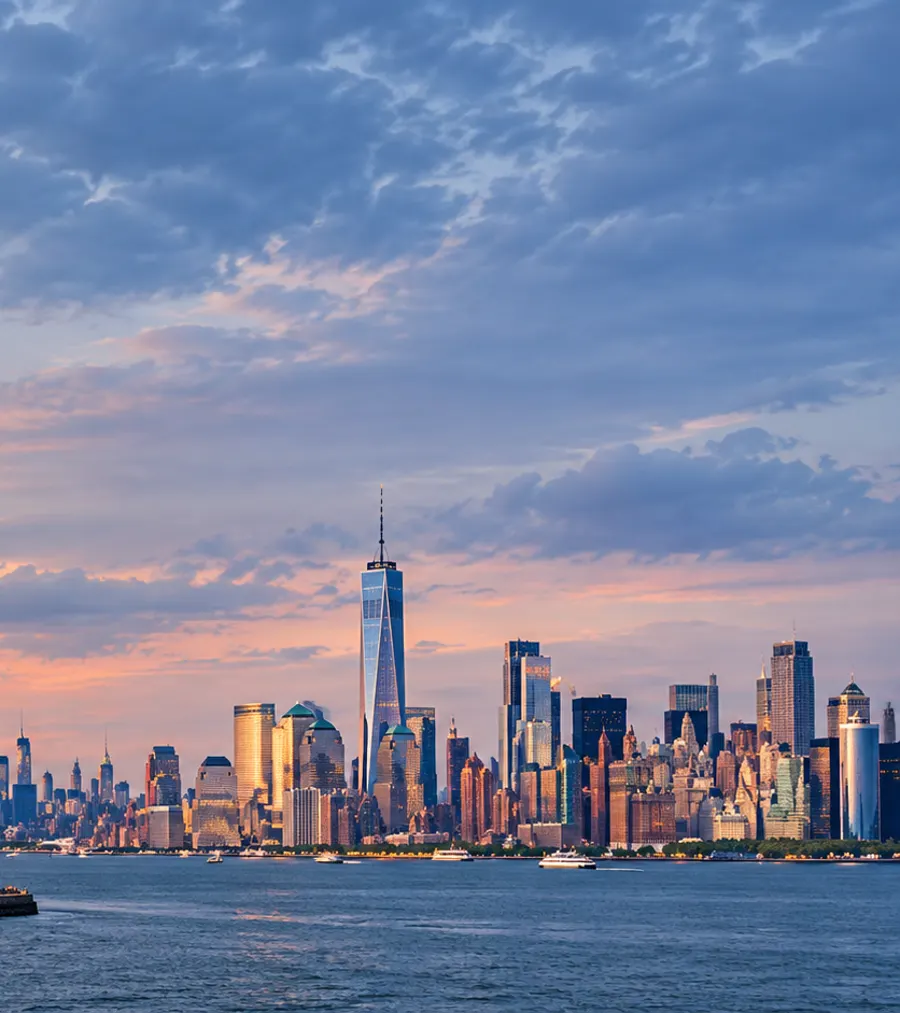
Bring a requirement →New York · Tuesday 3 November
14:06
Local time
What the rules say in the United States
From the United States market guide: the points that matter most for technology, data & cyber, each with the source it was checked against.
Full guide · Source-checked research100% of statements checked against a source127 checked against an official source2 checked against a secondary sourceChecked 2026-10-19Not yet professionally reviewed
The California Consumer Privacy Act applies to for-profit businesses doing business in California that have gross annual revenue over 25 million US dollars, or buy, sell or share personal information of 100,000 or more California residents or households, or derive 50% or more of annual revenue from selling California residents' personal information.
State law (California), not federal. Any one threshold is enough. Nonprofits and government agencies are generally not covered. The revenue figure is adjusted for inflation by regulation; the current adjusted figure was not confirmed on the source page.State of California Department of Justice, Office of the Attorney General · checked 2026-10-18Under the CCPA, consumers have rights to know, delete, correct, opt out of the sale or sharing of their personal information (including through a browser-based global privacy control) and limit the use of sensitive personal information.
California residents. Rights are subject to statutory exceptions.State of California Department of Justice, Office of the Attorney General · checked 2026-10-18The CCPA is enforced by the California Attorney General and the California Privacy Protection Agency; consumers can sue directly only after certain data breaches caused by a failure to maintain reasonable security, with statutory damages of up to 750 US dollars per incident.
Private action requires written notice and a 30-day cure period before suit. Applies to nonencrypted, nonredacted personal information.State of California Department of Justice, Office of the Attorney General · checked 2026-10-18California's regulations on cybersecurity audits, risk assessments and automated decision-making technology, together with other CCPA regulation updates, took effect on 1 January 2026.
California. Adopted by the California Privacy Protection Agency board on 24 July 2025 and filed with the Secretary of State on 22 September 2025. Some obligations are phased in after 1 January 2026; the phased dates were not confirmed on the page read.California Privacy Protection Agency · checked 2026-10-18All 50 states, the District of Columbia, Guam, Puerto Rico and the US Virgin Islands have laws requiring notification of individuals when a security breach involves personal information.
State and territorial laws; definitions, deadlines and regulator notice duties differ by state.National Conference of State Legislatures · checked 2026-10-18The US Department of Justice Data Security Program, issued under Executive Order 14117 and codified at 28 CFR Part 202, took effect on 8 April 2025 and prohibits or restricts certain transactions that give countries of concern or covered persons access to Americans' bulk sensitive personal data or US government-related data.
Federal. Applies to US persons, including US companies and their staff. Due-diligence, audit and reporting duties for restricted transactions took effect on 5 October 2025 per the DOJ page.US Department of Justice, National Security Division · checked 2026-10-18The countries of concern under the Data Security Program are China, Cuba, Iran, North Korea, Russia and Venezuela.
Federal. China includes Hong Kong and Macau under the rule's definitions (not confirmed on the section read). Covered persons also include entities owned, controlled or directed by these countries and individuals primarily resident in them.Office of the Federal Register (eCFR) · checked 2026-10-18Data Security Program bulk thresholds, counted over the preceding 12 months, are more than 100 US persons for human genomic data, more than 1,000 US persons for other human omic data and biometric identifiers, more than 1,000 US devices for precise geolocation data, more than 10,000 US persons for personal health or personal financial data, and more than 100,000 US persons for covered personal identifiers.
Federal. Government-related data is covered regardless of volume.Office of the Federal Register (eCFR) · checked 2026-10-18Read the full guide: Data protection, cross-border data and cybersecurity
Scope
Key questions
If your work involves another country or another area of expertise, WONE Global brings in the right professional and keeps all advisers informed.
WONE Global Partners in the United States
No named lead for Technology, Data & Cyber yet — these WONE Global professionals already work in the United States and can bring the right local colleague in.
South Carolina · United StatesWONE Global Partner · United States
Also in the United States
Appointed services show their named professional. Open positions link directly to the Expression of Interest form.
Cases
The cases this service leads or joins, each with what is at stake, how WONE Global handles it and who handles it in the United States.
WONE Global Intelligence
Ask in your own words. Answers come from WONE Global's checked records, with every source shown, and end with the named Partner who can act. Go deeper on any point, or build a decision file.
Contact WONE Global
Save your questions, decisions and WONE activity in one account.
Forgot your password? Reset it securely.
Partner workspaces are for Partner firms. Explore partnership →
